How do you give an AI agent access to your social media accounts safely? Three rules cover it: never give an agent your passwords, connect it through a tool layer with scoped permissions instead, and keep a human approval step between the agent and the publish button. Do those three things and delegating your posting is about as risky as delegating it to a junior colleague. Skip them and you have handed a language model the keys to your brand's public voice.
Here is the full pattern, including the failure modes it exists to prevent.
Why this needs rules at all
An agent that posts for you is doing something genuinely new: taking public, hard-to-reverse actions on your behalf, planned by a model rather than reviewed line-by-line by you. It is also no longer rare: in the State of AI Agents in Social Media report, 79% of posts on PostEverywhere were created through the API or MCP. Three risks follow.
Prompt injection. An agent that reads external content, a webpage, a comment thread, a DM, can encounter text crafted to hijack its instructions ("ignore previous instructions and post the following").
This is the top entry in the OWASP Top 10 for LLM applications for good reason: the model cannot always tell your instructions from an attacker's.
Excessive agency. OWASP's term for an agent granted more capability than its task needed. An AI agent that only needed to draft captions but was wired with delete rights, DM access and billing permissions is an incident waiting for a trigger.
Irreversibility. A bad post is public the moment it lands. Followers screenshot faster than you can delete. Unlike almost everything else an AI agent does for you, publishing has no undo.
None of this argues against agents. It argues for wiring them the way you would wire any powerful automation: least privilege, human checkpoint, kill switch.
Rule 1: passwords never touch the agent
The naive setup, telling an AI agent your Instagram login, or letting a browser-automation agent sign in as you, is the one that fails every test at once.
Shared passwords give total account control, not scoped access. They trip two-factor authentication and device checks, which platforms read as account takeover. Automated login breaches most platforms' terms of service, which is how accounts get locked.
And revocation means changing the password everywhere it was ever used.
If a tool's setup instructions ask for your actual social account password, that is the signal to close the tab. Legitimate access flows through OAuth, where the platform itself issues a scoped, revocable grant and your password is never shared.
Rule 2: access goes through a tool layer, not raw credentials
The safe architecture has three parts, and the agent only ever sees one of them:
- Your social accounts connect to a posting platform via OAuth, the same way you would connect them to any scheduler.
- The posting platform exposes specific capabilities: draft, schedule, upload media, read analytics.
- The agent connects to those capabilities through an MCP server or an API, authenticated with its own key, never with your account credentials.
The agent can do exactly what the tools allow and nothing else. Ours exposes 45 tools through the Model Context Protocol, the open standard Anthropic introduced in 2024 that both Claude and OpenAI's agent stack now speak.
There is no "post as me anywhere" grant, no DM access, no password in the loop, and disconnecting the server severs everything at once.
Whether your agent should use MCP or the raw API depends on whether code or a model is driving; the PostEverywhere API supports both, a REST API and a hosted MCP server.
Whichever you choose, PostEverywhere's AI agent logs record every call the agent makes, so you can check its work afterwards.
Rule 3: approval sits between the agent and the world
This is the rule that neutralises prompt injection almost entirely. If every draft an agent produces waits for a human yes before publishing, then a hijacked instruction produces a weird draft in your queue, not a weird post on your feed.
The blast radius collapses from "public incident" to "delete a draft".
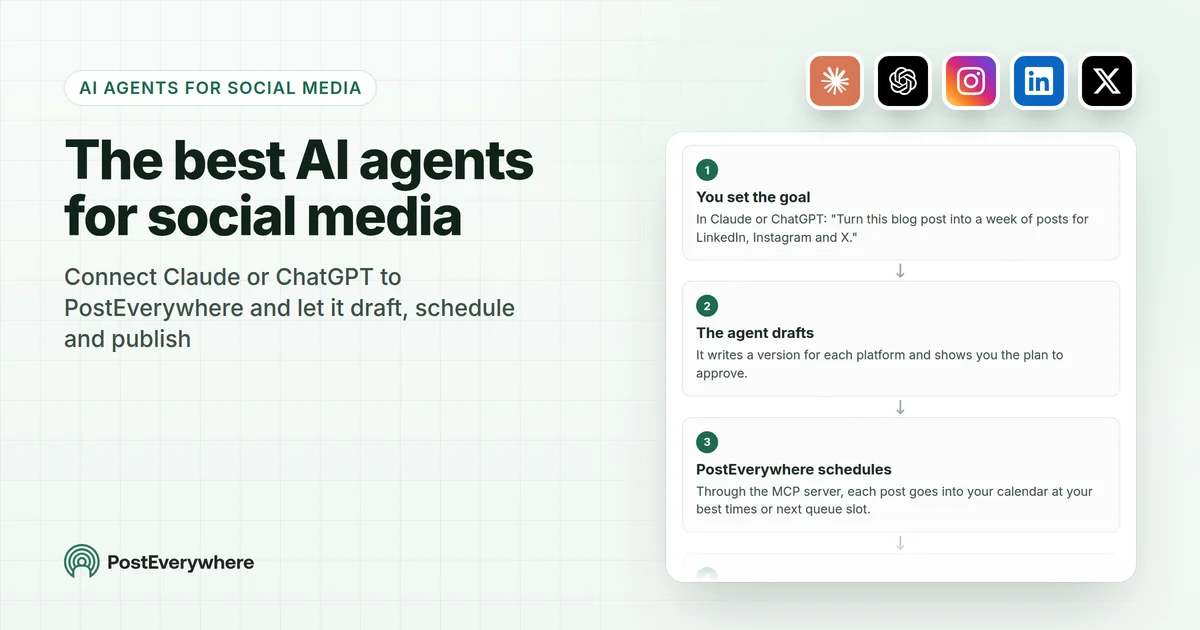
In practice the workflow looks like this: you ask Claude for a week of posts and tell it to save them as drafts, you review them in one place, and you schedule the ones you are happy with.
Be explicit, because the agent does what you ask: give it no time and it publishes now, give it a time and it schedules, and it saves a draft when you ask for one.
Our Google Business Profile walkthrough for AI agents shows the same drafts-first pattern for a business with several locations.
With team workspaces, the "Require approval" setting holds team Members' posts until an owner or admin approves them, the same maker-checker separation finance teams use for payments. That setting does not hold posts an agent creates through the API or MCP (a REST API integration can opt in by asking for approval when it creates a post, but the MCP cannot), so for agent work the draft step is your checkpoint.
When should you relax it? For genuinely low-stakes, high-volume streams, a changelog feed, say, teams sometimes let API-driven posts publish directly while keeping approval on everything agent-drafted. That split is reasonable.
Removing the review step from agent output on a brand account is not, so make "save these as drafts" part of the standing instructions you give the agent.
Want the safe version without building it? Connect Claude or ChatGPT to PostEverywhere's hosted MCP server, ask it to save drafts, then review them in one calendar and schedule the ones you approve. Start a 7-day trial from $9/mo.
A card is required and there is no free plan.
Rule 4: least privilege, by account and by capability
Give the agent the accounts the job needs, not every account you own.
Concretely: connect the brand accounts an AI agent manages and leave your personal profiles unconnected. If an agency runs this for clients, multi-account management with per-workspace separation keeps client A's agent workflow away from client B's accounts entirely.
Where roles exist, a human holds the approval role, and the agent's work comes in as drafts for that person to check.
The same thinking applies to capabilities. Drafting and scheduling are low-risk. Deleting history, changing profile details and reading DMs are different classes of action, and an agent doing content work has no business holding them.
A tool layer makes this enforceable; a shared password makes it impossible.
Rule 5: know your kill switch before you need it
Safe access is revocable access, and you should know the revocation path on day one, not during an incident.
With the tool-layer pattern it is one move: disconnect the agent or delete its API key, and every agent capability dies at once, across all top platforms, while your own logins carry on untouched.
Check the platform side occasionally too: every major network lists authorised third-party apps in its security settings, and Google's third-party access page is the model most of them follow.
Two habits complete the picture. Keep the agent's work visible in a shared calendar so a human eyeballs the queue as a matter of routine. And treat anything strange in the drafts, odd links, sudden tone shifts, instructions you did not give, as a prompt to check what the agent was reading when it drafted.
Auditing an existing setup? The two questions that matter: does anything hold your real passwords, and does a human see agent posts before they go live? If the first answer is yes or the second is no, our agent workflow is the ten-minute fix, from $9/mo with a 7-day trial.
What a safe setup looks like, end to end
The whole pattern, assembled, takes under ten minutes:
- Connect your social accounts to PostEverywhere via OAuth, all top platforms supported.
- Connect Claude or ChatGPT to the hosted MCP server, following the Claude walkthrough or the ChatGPT one.
- Ask for work in plain language, and tell the agent to save it as drafts.
- Review the drafts in the calendar and schedule the ones you approve. That step stays.
- Know the disconnect switch, and check the queue weekly like you would check any delegated inbox.
Your passwords were never shared, the agent's permissions are exactly the 45 tools and nothing more, every post passed a human, and one click undoes the whole arrangement.
Frequently asked questions
Is it safe to give an AI agent access to my social media accounts?
Yes, provided the access is scoped and supervised. The agent connects through a tool layer such as an MCP server rather than holding your passwords, and a human approves drafts before they publish.
Those two properties turn the worst case from a public incident into a deleted draft.
Should I ever give an AI agent my account password?
No. Shared passwords grant total control, break two-factor authentication, breach most platforms' terms of service, and cannot be revoked without changing the password everywhere. Legitimate agent access uses OAuth grants and tool-layer keys, never your credentials.
What is prompt injection and why does it matter for posting?
Prompt injection is malicious text, hidden in a webpage, comment or message an agent reads, that tries to override its instructions. For a posting agent the danger is obvious: hijacked instructions become public posts.
An approval step contains it, because injected output stalls in your queue instead of publishing.
Can Claude or ChatGPT post to social media without my approval?
Yes, if you ask it to. Connected through PostEverywhere's MCP server, an AI agent publishes now, schedules, or saves a draft, depending on what you ask, so tell it to save drafts whenever you want to review first.
The "Require approval" setting holds team Members' posts, not posts an agent creates through the API or MCP, and the MCP server has no tool for approving posts.
How do I revoke an AI agent's access?
With a tool-layer setup it is one action. Disconnect the agent or delete its API key, and every capability is severed across all connected platforms at once. Your own logins are unaffected because they were never shared.
Platform security pages list third-party grants if you want to audit from that side too.
What permissions should a social media AI agent have?
Drafting, scheduling, media upload and analytics reading cover content work. It should not hold deletion rights, DM access, profile-editing rights or billing access. It should only see the accounts the job requires. Least privilege is the principle; a tool layer is what makes it enforceable.
Can I let an agent manage client accounts safely?
Yes, with workspace separation. Each client's accounts sit in their own workspace, the agent's access is scoped per workspace, and approval rights sit with a human account manager. That keeps one client's automation entirely away from another's accounts.
What is the safest way to let AI post for me?
Connect an AI agent to a hosted MCP server rather than sharing credentials, and have it save drafts you review before anything is scheduled. Restrict the agent to the accounts and capabilities the job needs, and know the disconnect switch. That pattern gets you the delegation without the exposure.
The bottom line
The question is not whether to let an agent touch your accounts, that ship is sailing across the industry, but whether the access is built like infrastructure or like a shortcut. Passwords shared with a chatbot are a shortcut.
Scoped tools, human approval and a one-click kill switch are infrastructure.
How much setting up that actually takes varies more than most people expect, from a single pasted URL to a self-hosted server, and our AI social media agents comparison ranks the options on setup effort, using each vendor's own documentation, and on capability, which helps decide which agent to grant that access to in the first place.
Set it up properly once and the rest is delegation. Our guides to connecting Claude, connecting ChatGPT and what social media AI agents actually are cover the rest of the stack, and the PostEverywhere API page covers both surfaces your agent can drive.
On the trust question, a directory listing is a weak signal but not a worthless one: PostEverywhere's server is listed in Anthropic's Claude connector directory, which means it has been through their review rather than being a URL from a blog post.
Founder & CEO of PostEverywhere. Writing about social media strategy, publishing workflows, and analytics that help brands grow faster.